When a browser opens a secure website, it needs a way to encrypt the connection and check that it is speaking to a server authorized for that domain. A digital certificate helps perform both tasks.
The process happens quickly, usually before the page appears.
The certificate binds a name to a key
A certificate contains a domain name, a public cryptographic key, an expiration period and information about the organization that issued it. The server presents the certificate during the opening exchange with the browser.
The browser checks whether the requested domain is covered, whether the certificate is currently valid and whether its signatures lead through a trusted chain to a recognized certificate authority.
Trust is built through a chain
Browsers and operating systems maintain stores of trusted root authorities. Those roots can authorize intermediate authorities, which then issue certificates to websites. Each link is signed so the browser can verify that the chain has not been altered.
This system avoids requiring every browser to know every website in advance. It also creates responsibilities for authorities to confirm domain control and respond when keys or certificates are compromised.
The connection negotiates its own secrets
The public key helps the browser and server authenticate the exchange and establish temporary session keys. Those session keys encrypt the actual traffic. Modern protocols are designed so that learning the server's long-term key later should not automatically expose previously recorded sessions.
A certificate warning can appear when a name does not match, a certificate has expired or the chain cannot be trusted. Bypassing such a warning removes an important identity check.
A secure connection is not a character reference
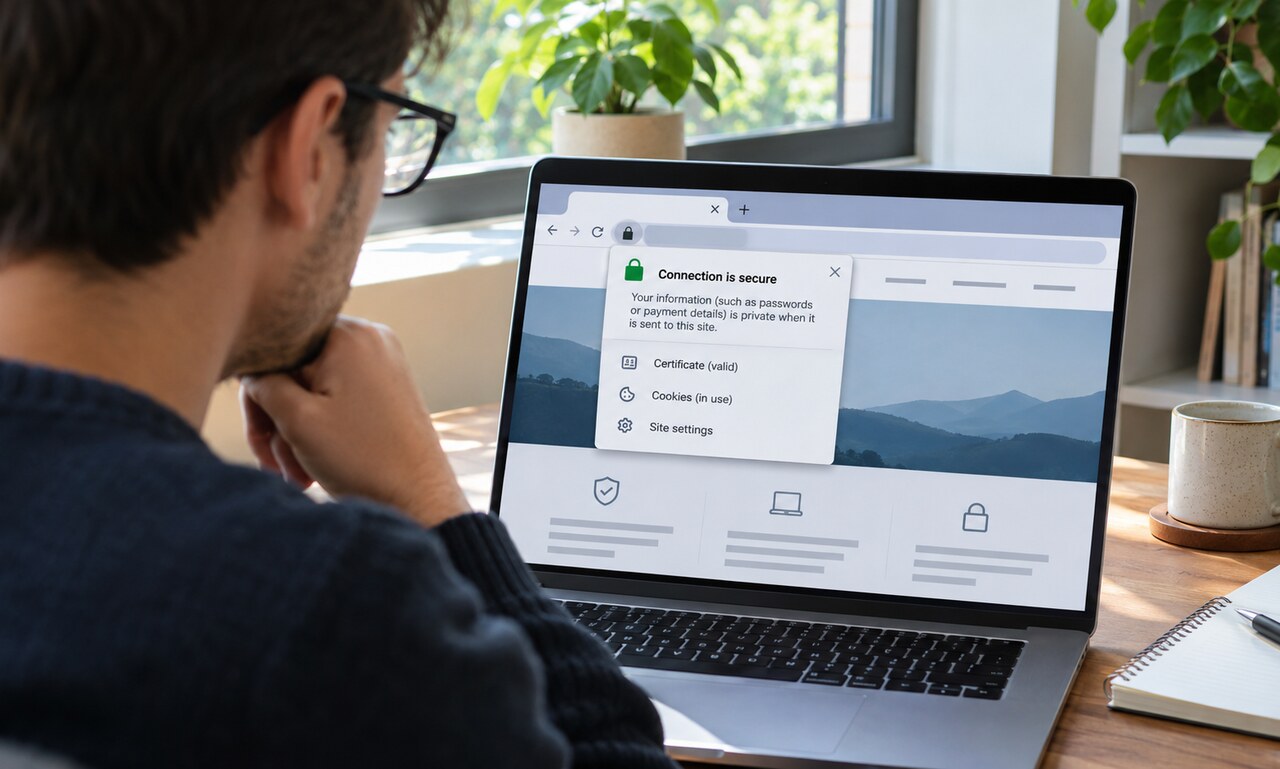
A valid certificate means the connection to the named domain is encrypted and authenticated according to the certificate system. It does not prove that the business is honest, the article is accurate or a download is safe. A deceptive site can obtain a valid certificate for a domain it controls.
That distinction explains why browsers moved away from presenting the lock as a broad symbol of trust. Certificates protect the path between browser and site. Judging what the site asks, promises or provides remains a separate decision.
READ NEXT